I have been testing the Send feature and I encountered some issues:
- Password protection does not work at all. I cannot access the Send because the password I set is never accepted. The password seems to actually be blank (that is what I see in the Android app when I look at the details of the Send I created with SailWarden) instead of the password I set when I created the Send. This might be directly related to the next issue (#2).
- When creating a new Send, several fields are not saved/shown:
- when accessing the Send, hide the text by default - NOT saved at all (can’t see it in the Android bitwarden app either)
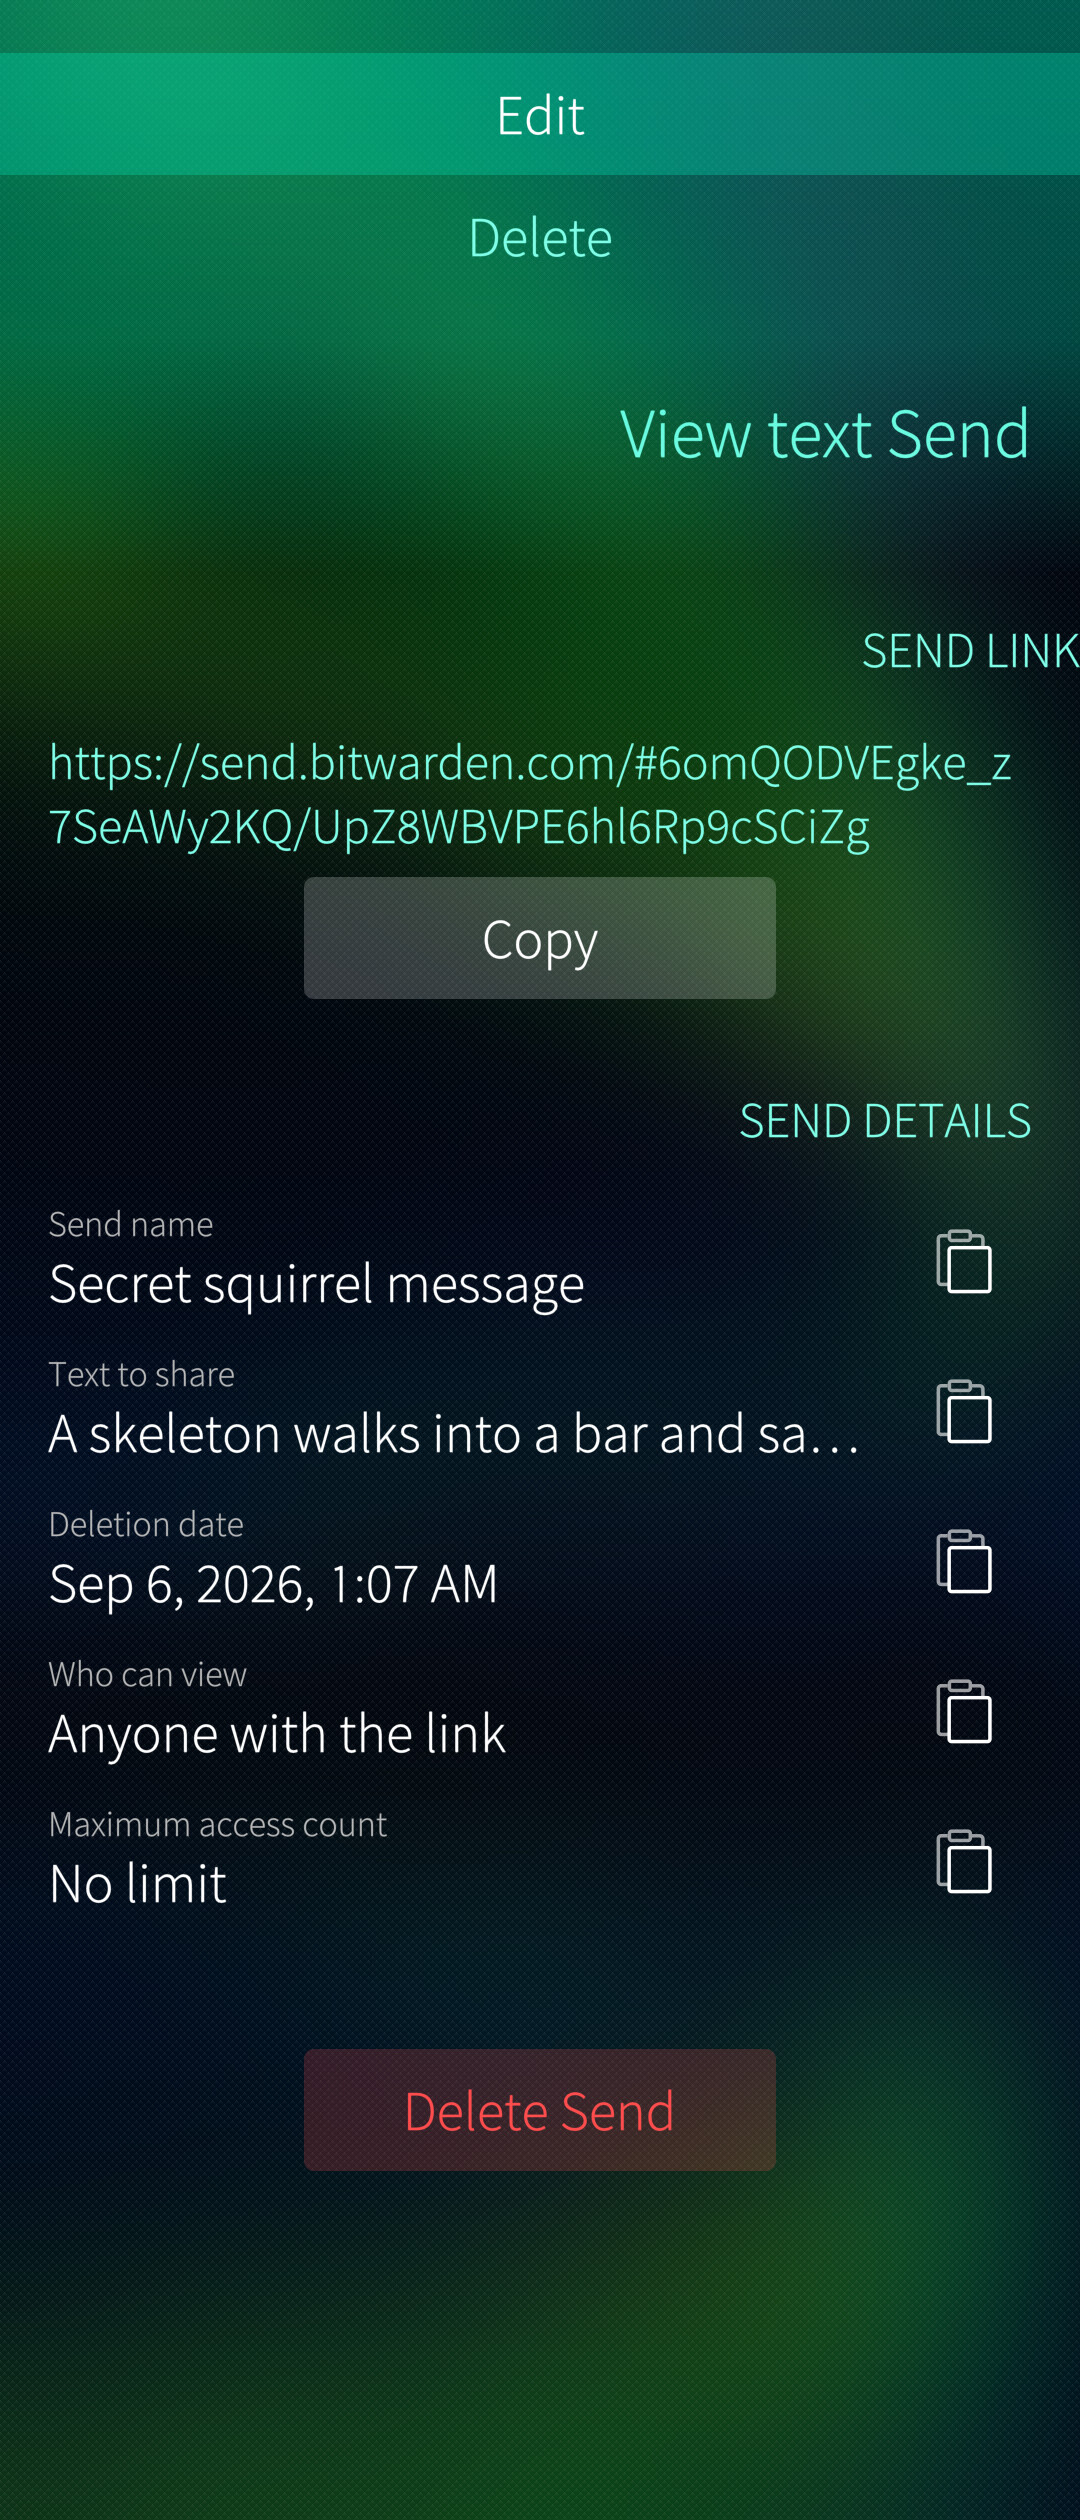
- deletion date - saved, visible when viewing an existing Send, NOT shown correctly when editing an existing Send
- maximum access count - same as above: saved, visible when viewing, NOT shiwn when editing
- hide my email address from recipients - saved, NOT shown when editing
- private notes - saved, NOT shown
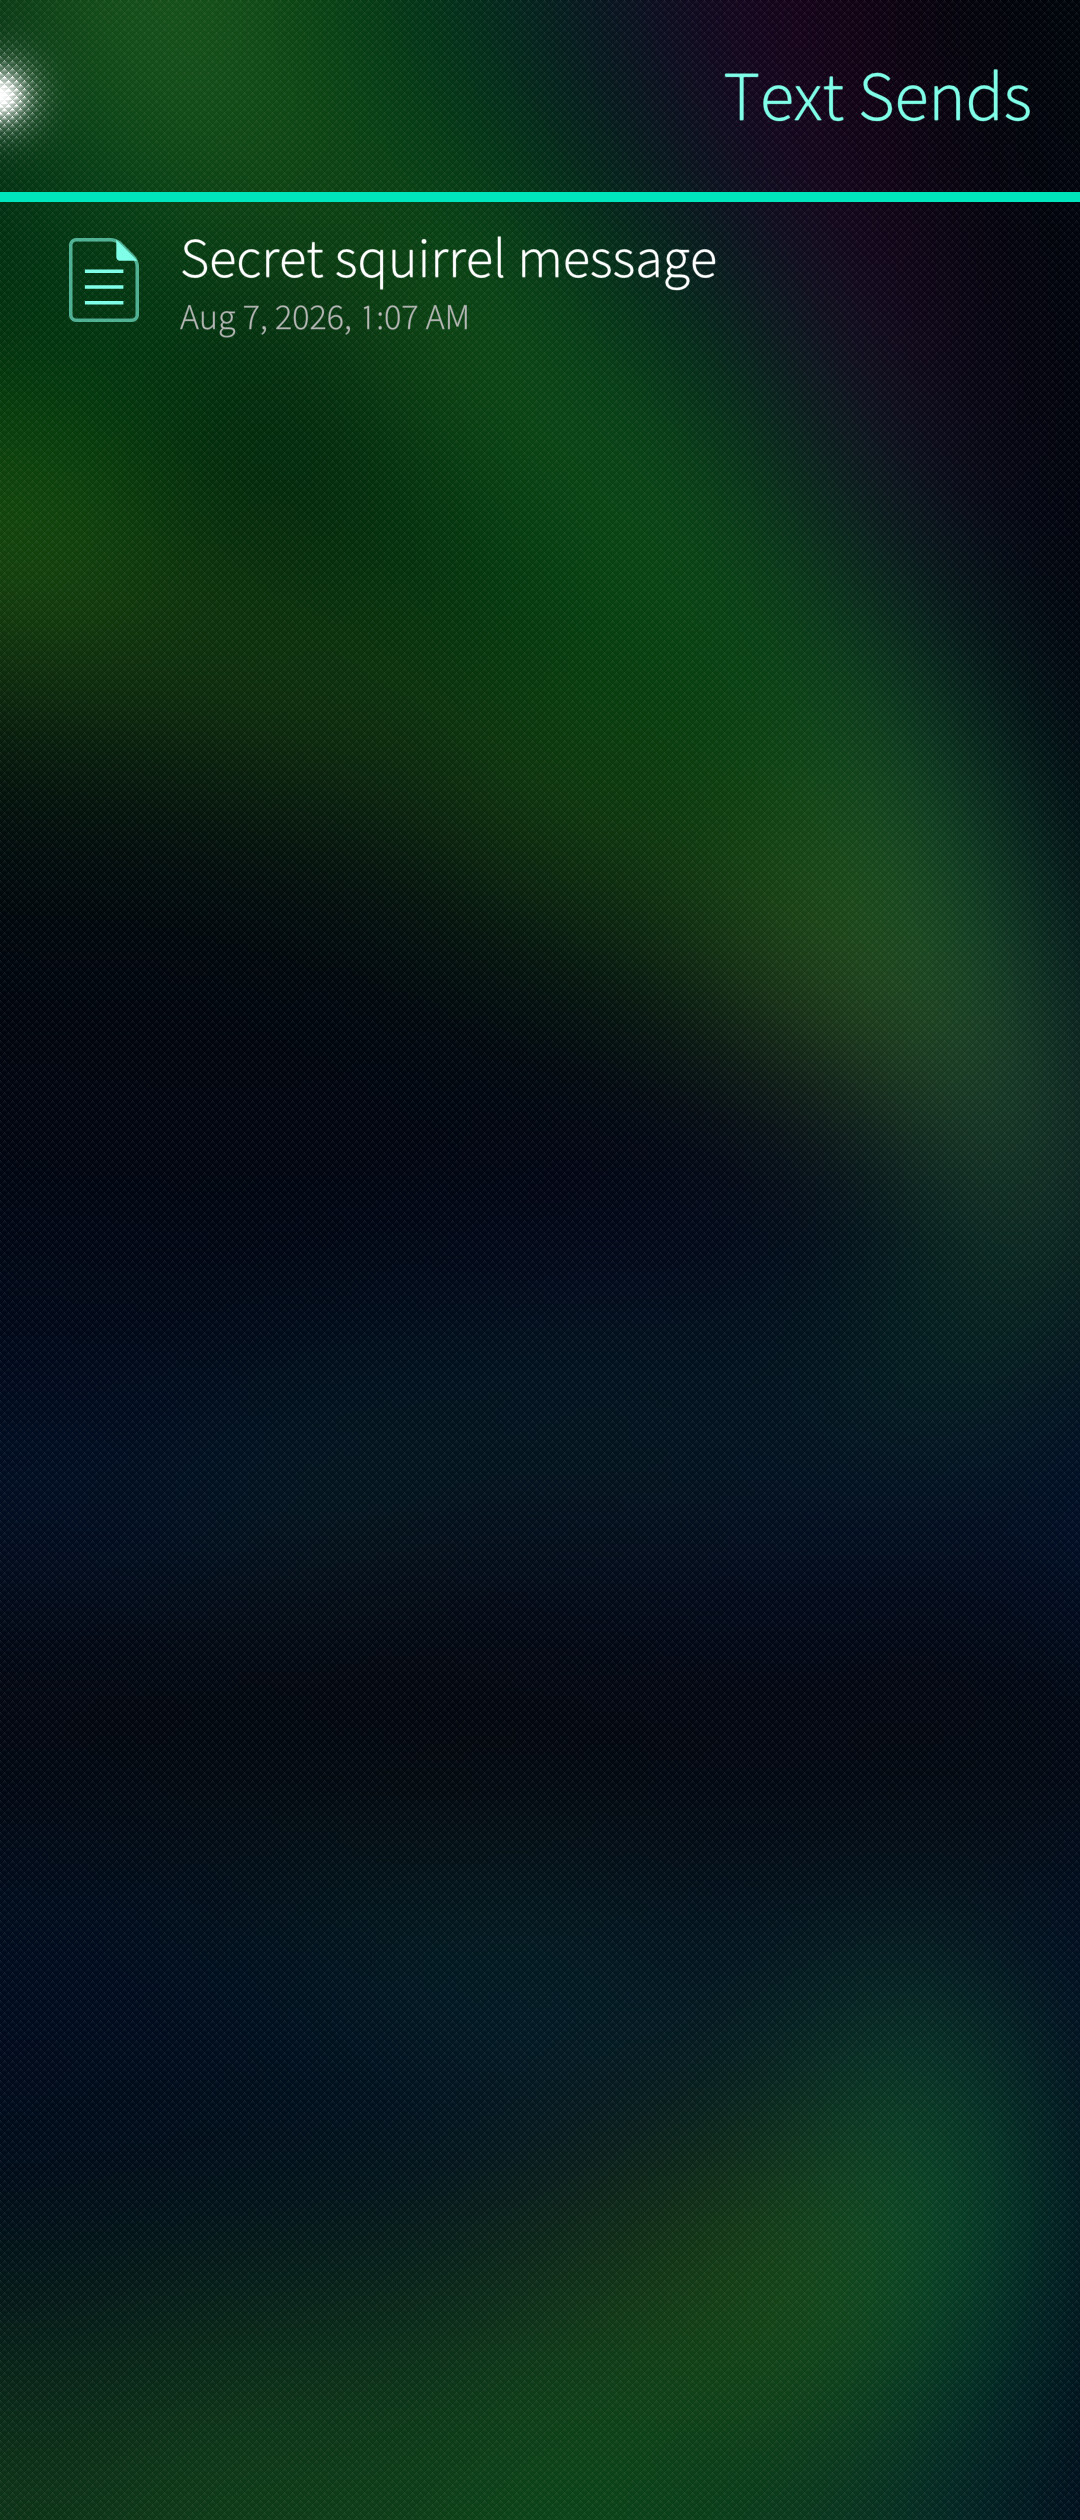
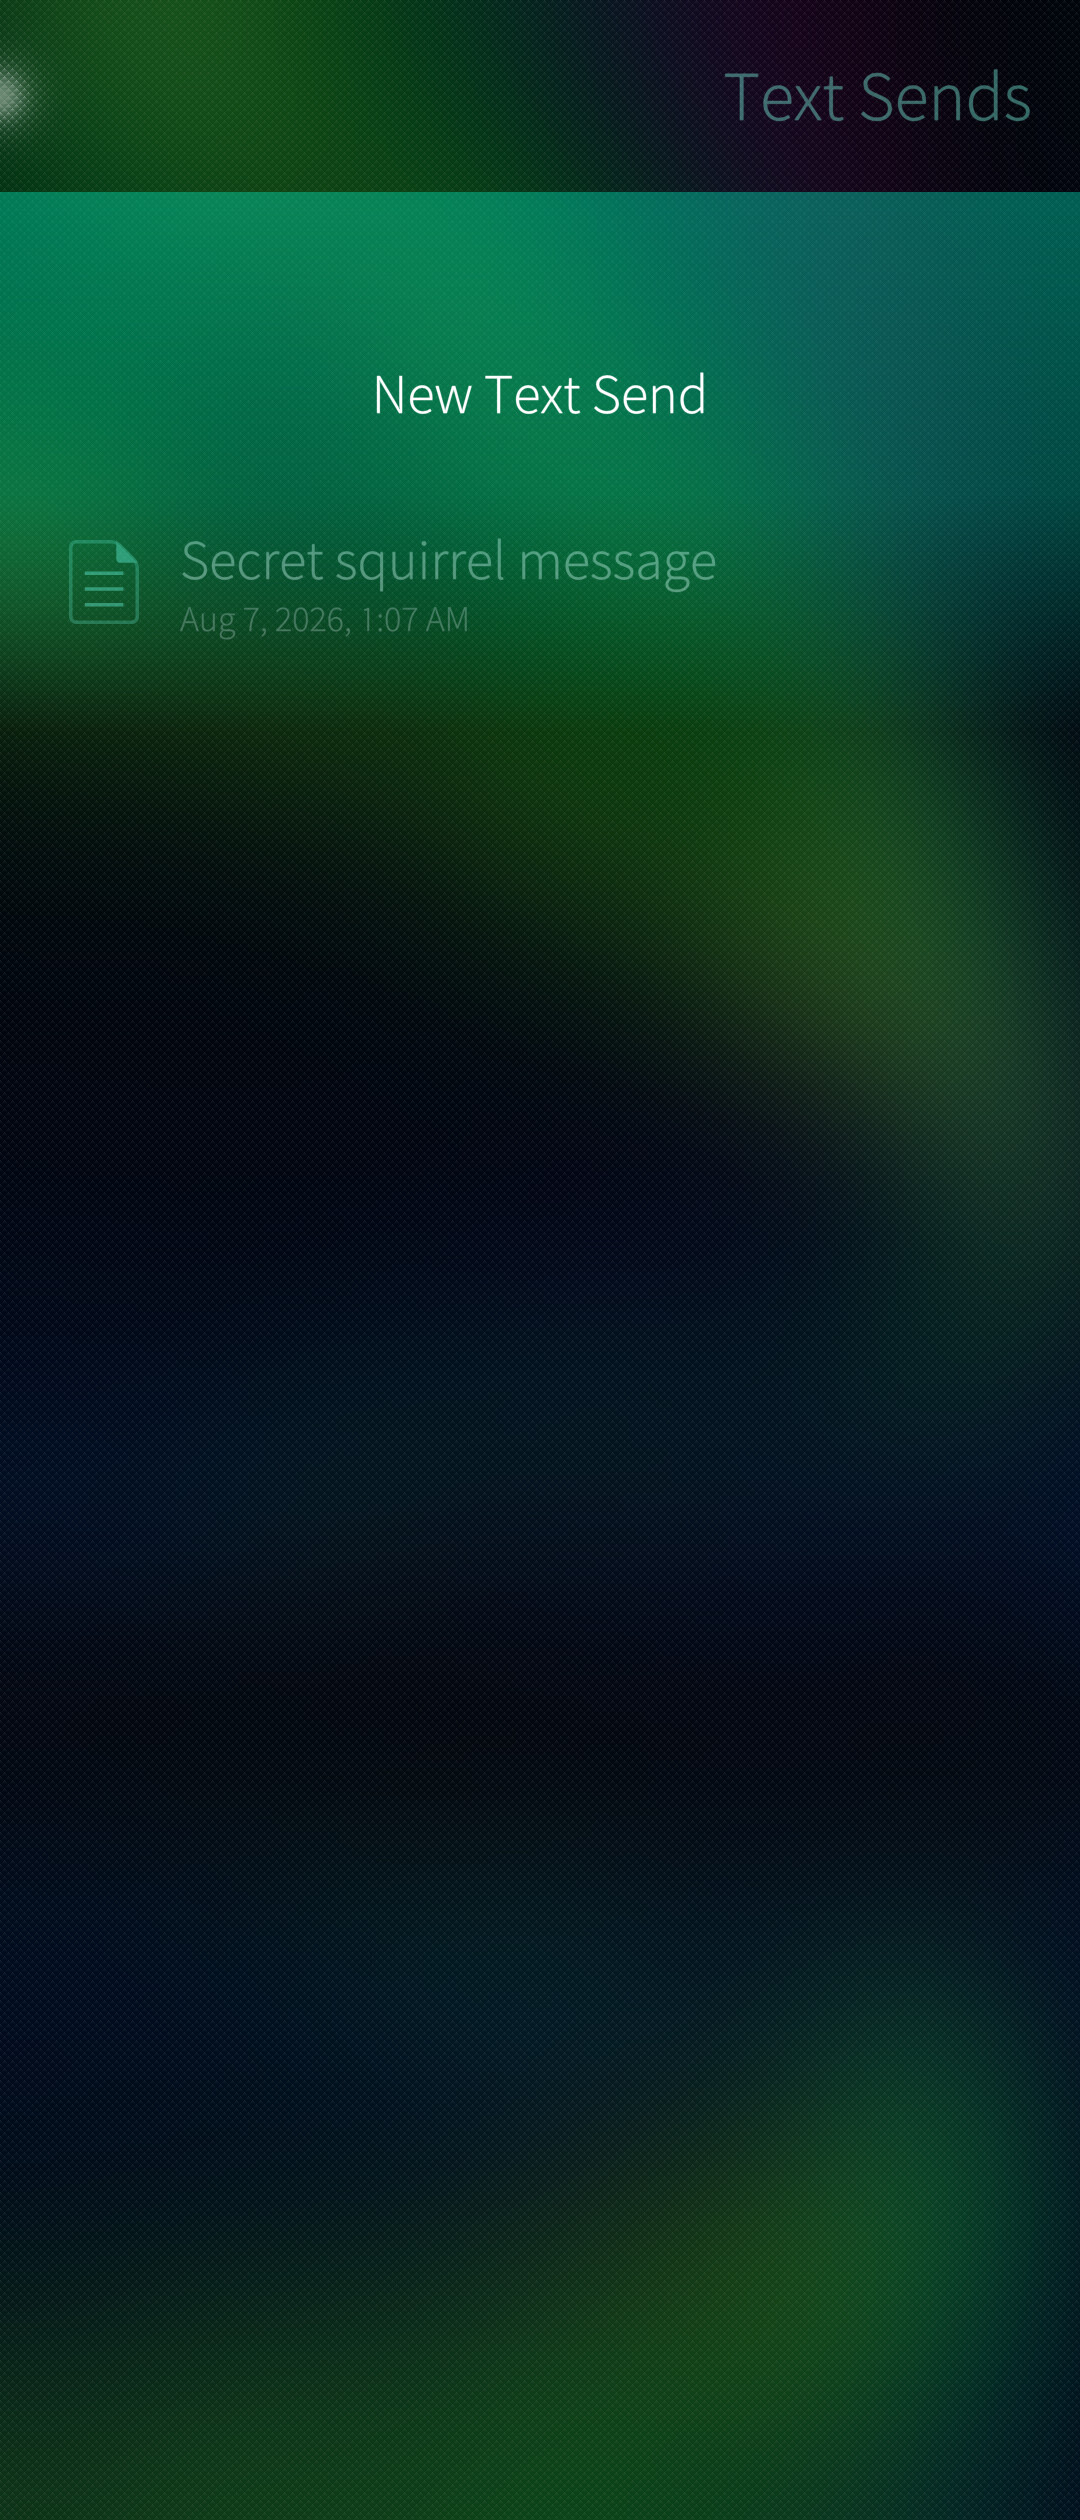
- On the Text Sends page the pulley menu is not at the top of the page AND does not contain a search option (it should)
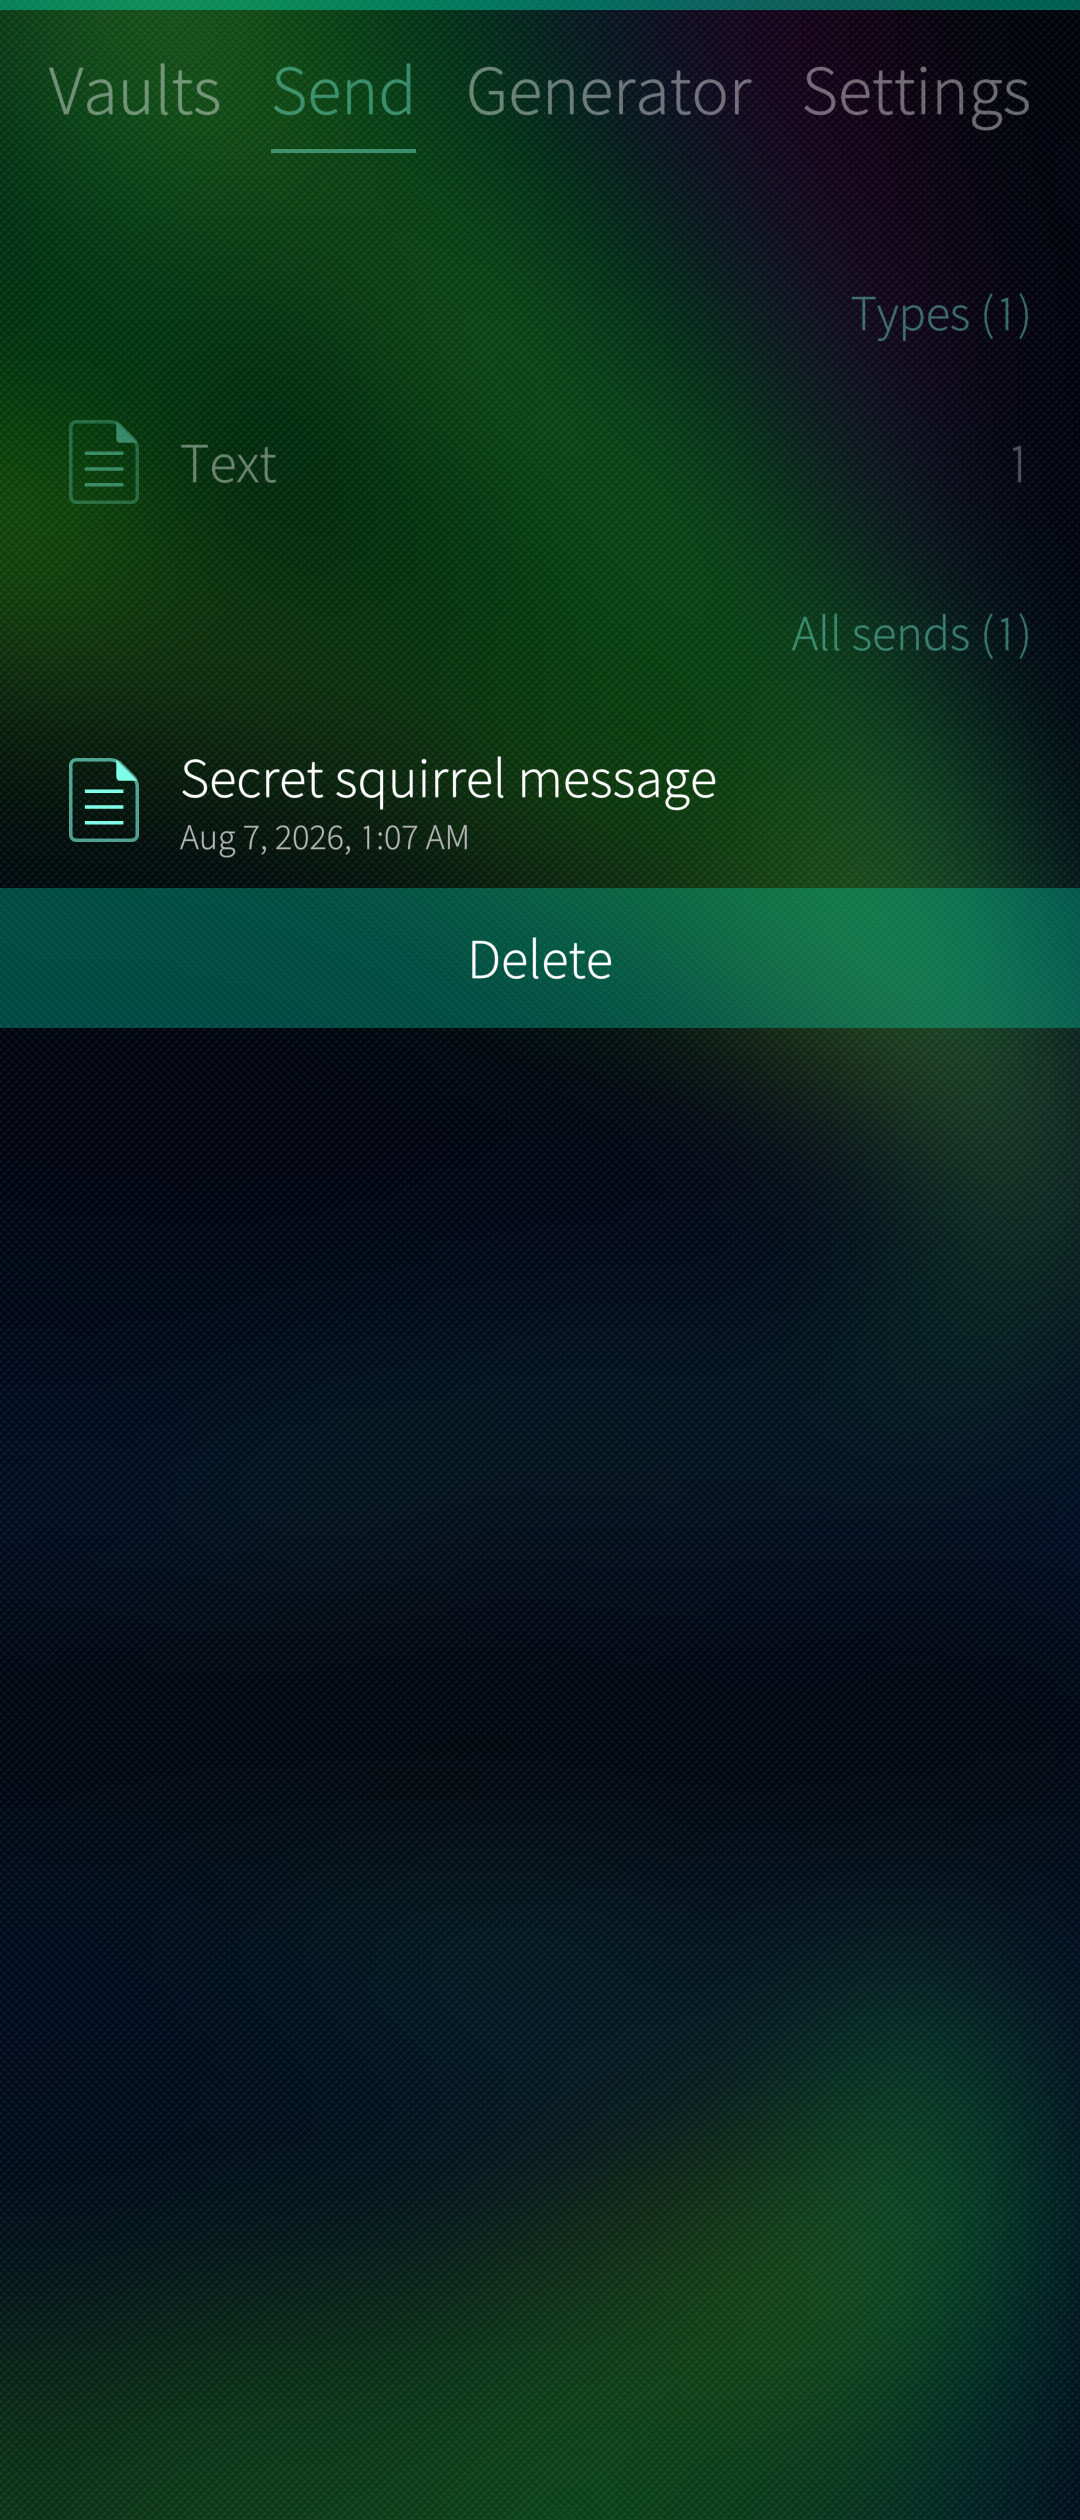
- When deleting a Send from the main view of the Send tab, by long pressing the Send to show the context menu, no Undo timer is shown. The send is deleted instantly. In the other places from where a Send can be deleted, an undo timer is shown (as expected).
- When viewing the Text Send, the sections are written in all caps AND thw order of the menu items is not great (Edit should be the first item when pulling the menu)
Unrelated to the Send functionality, the password generator seems to sometimes generate 4-character passwords even if the length is set to 5.
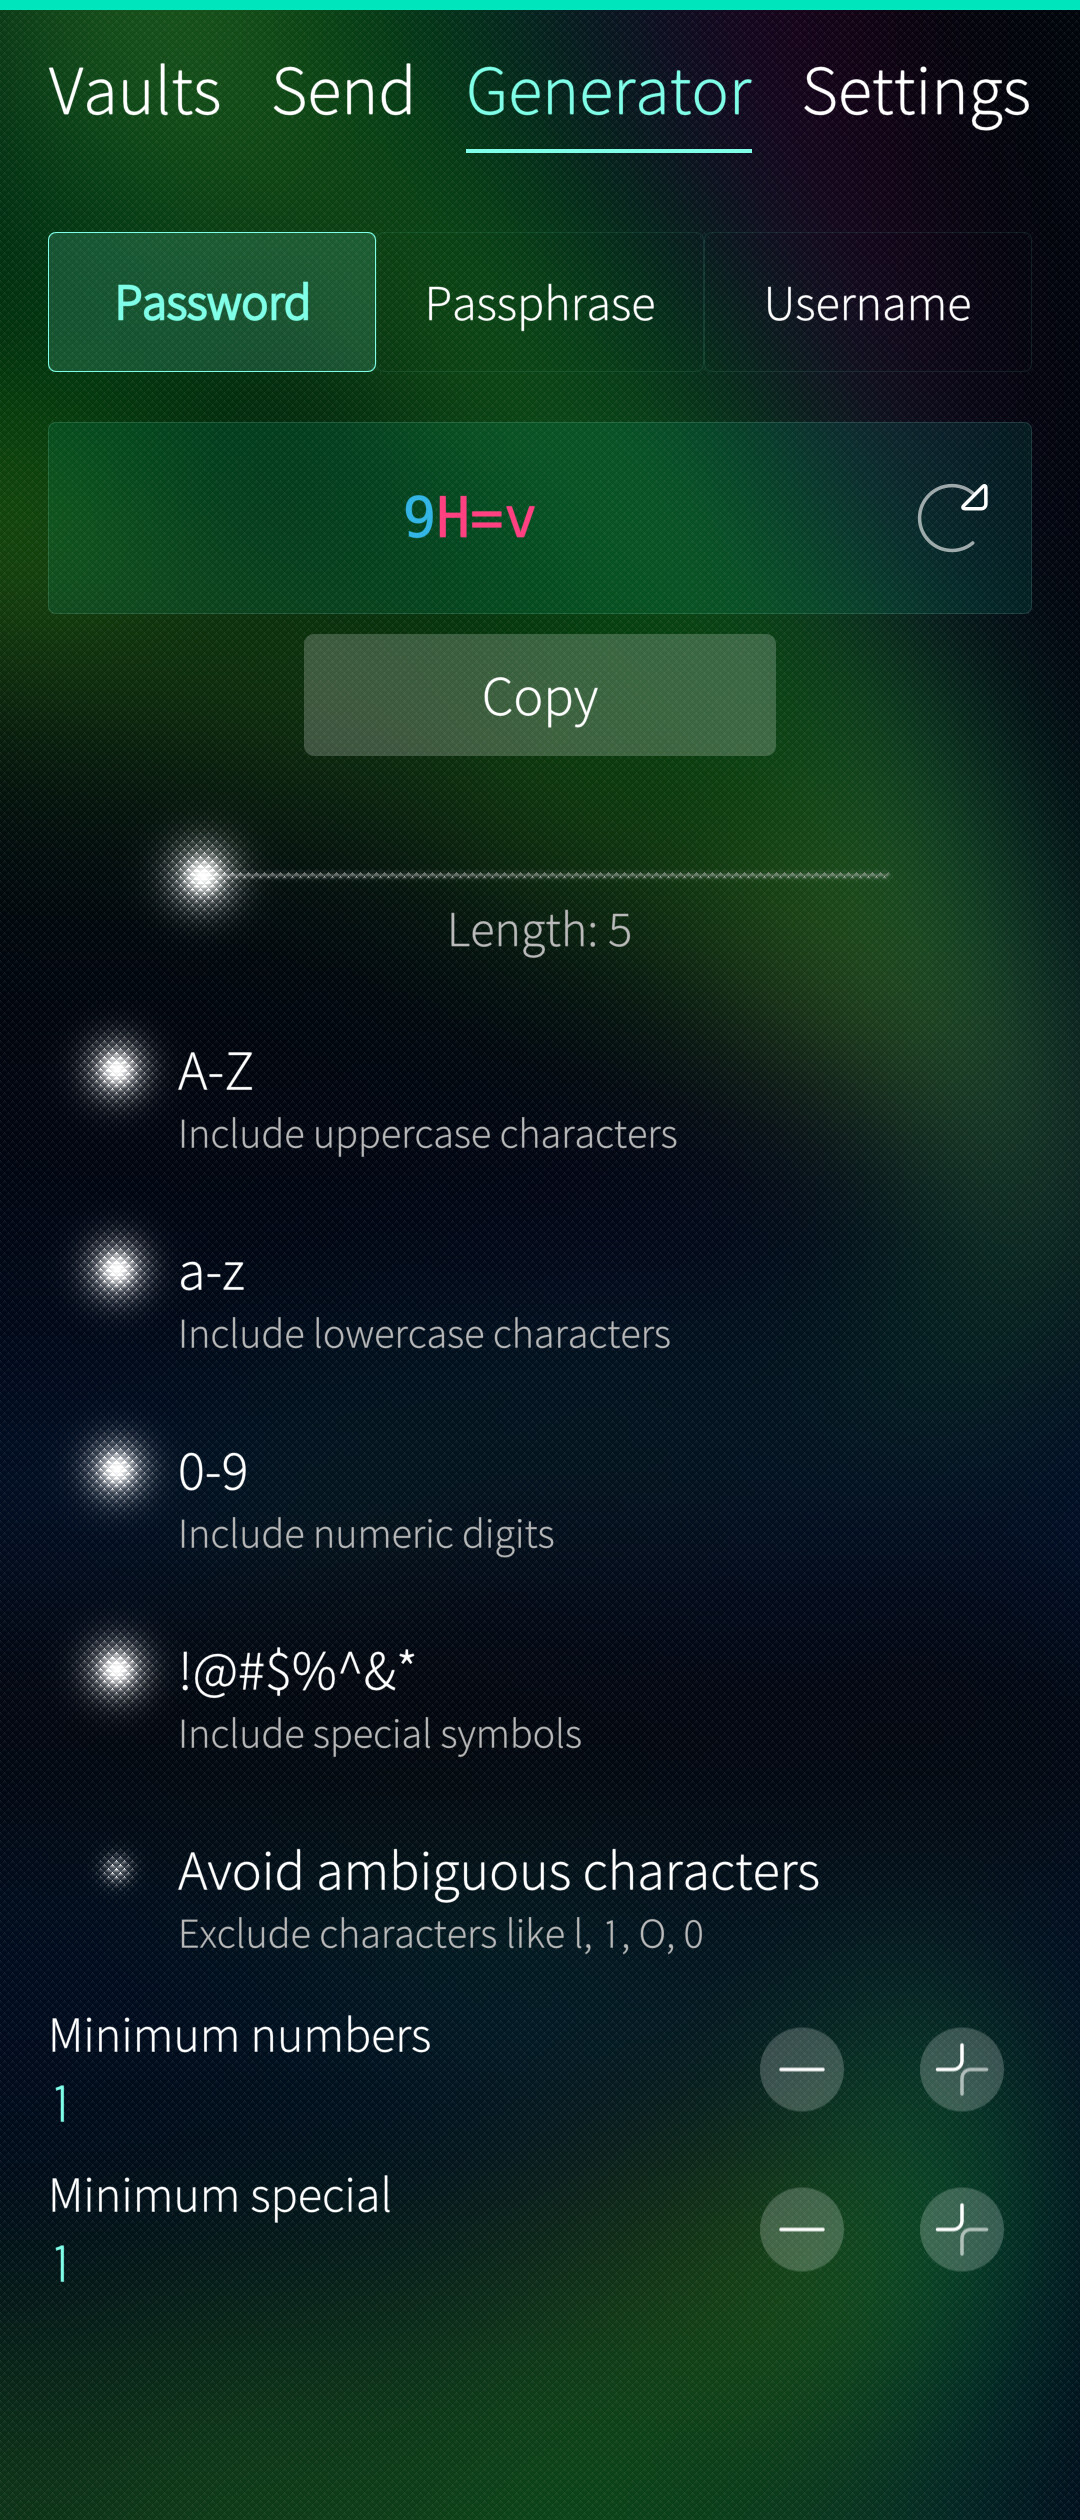
Every once in a while, but not that rarely, a 4-character password is generated while tapping the refresh button that generates a new password.
I don’t know if something similar also happens for longer passwords. I haven’t tried it, because it is not easy to spot.
The first thing I can think of is to add an assert for each password generation to check if the length of the generated password matches the length specified by the user, so it is easier to catch the bug in action.